
Tag: AI model defense
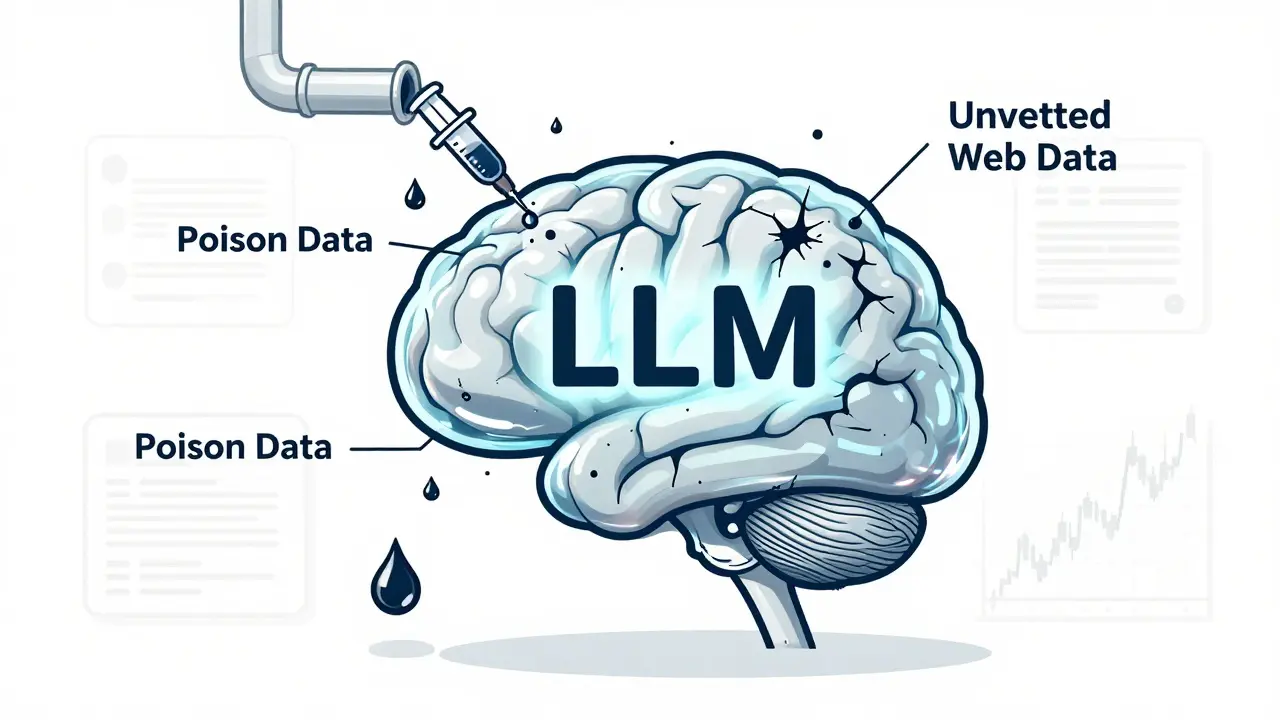
Training data poisoning lets attackers corrupt AI models with tiny amounts of fake data, leading to hidden backdoors and dangerous outputs. Learn how it works, real-world cases, and proven defenses to protect your LLMs.
Categories
 Artificial Intelligence
Archives
Recent-posts
Vibe Coding for Product Managers: Build Working Prototypes in Hours, Not Weeks
Jul, 28 2026
Interoperability Patterns to Abstract Large Language Model Providers
Jul, 22 2025
Dependency Injection in Vibe-Coded Backends: Testability and Modularity
May, 26 2026
Image-to-Text in Generative AI: How AI Describes Images for Accessibility and Alt Text
Feb, 2 2026
Service Level Objectives for Maintainability: Key Indicators and How to Set Alerts
Mar, 16 2026